From PADS4 2025.2 onward, this feature is part of PADS4 CTRL Center. For more information, see CTRL Center > Administration > Identity.
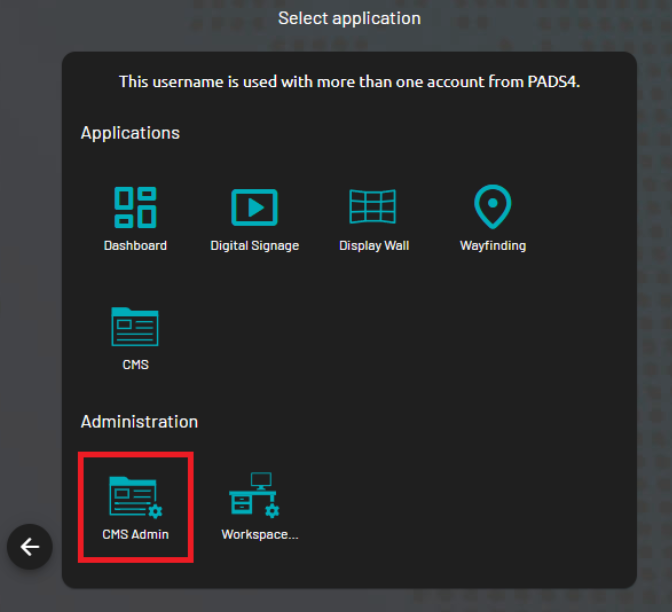
This manual can only be followed if you have configured SSO in your Azure / Entra ID environment.Now that all of the above information has been gathered, PADS4CMS can now be configured to make use of SSO.
In order for SSO to function correctly, PADS4 must be configured with use of HTTPS. In order to achieve this, you would need to follow this guide with use of an SSL certificate.
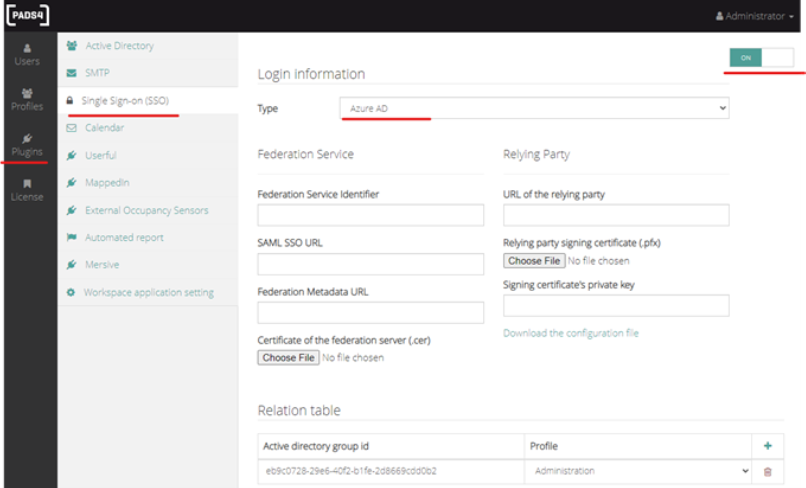
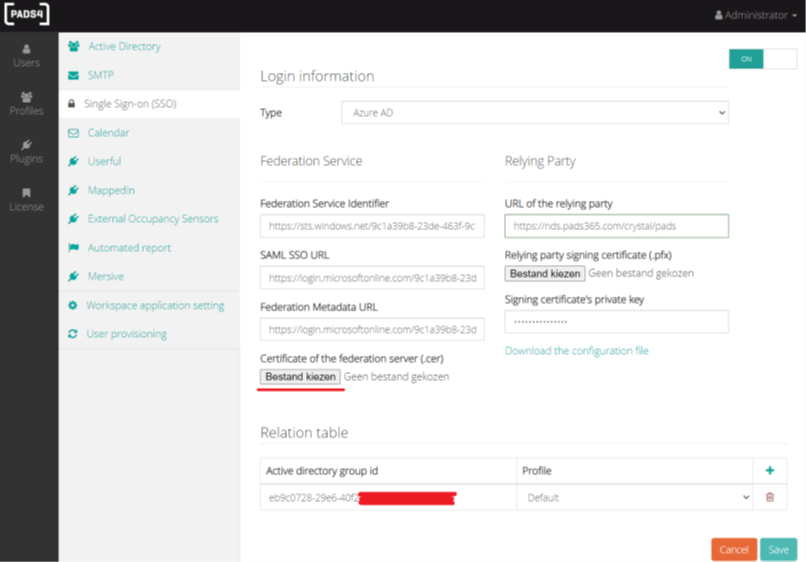
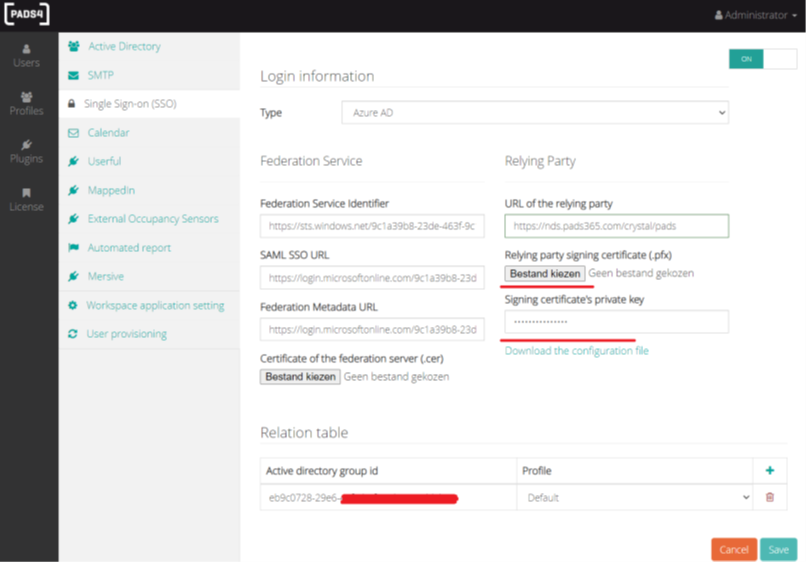
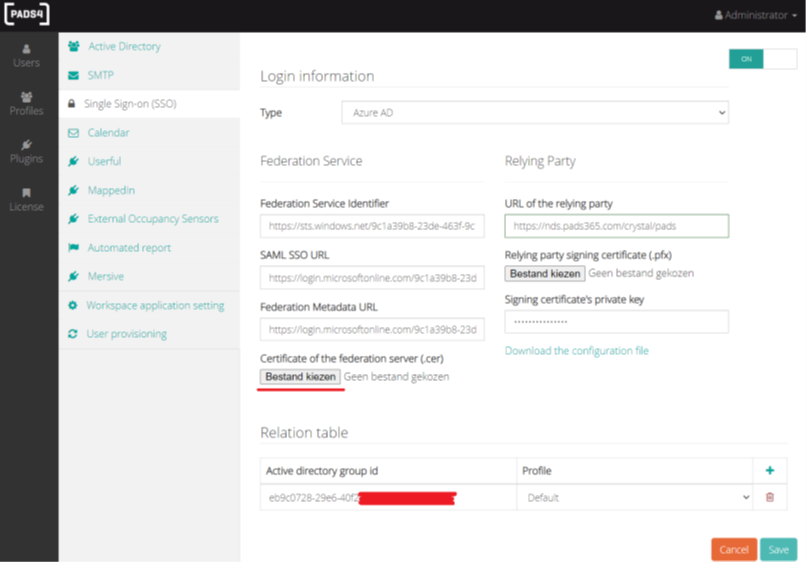
The copied string for the “ URL of the relying party ” in the CMS SSO configuration should not contain**“ /Saml ”** as copied from Azure butrather only**“ /crystal/pads ”** .(Where “pads” is the default domain) Example: The Azure copied link looks like this:https://robin.pads365.com/crystal/pads/Saml2however, it should be like this insteadhttps://robin.pads365.com/crystal/padsUpload the Application Certificate (Raw) that you have downloadedfrom Azure here:
Step 4 : Upload the Application Certificate (Raw) that you have downloaded from Azure
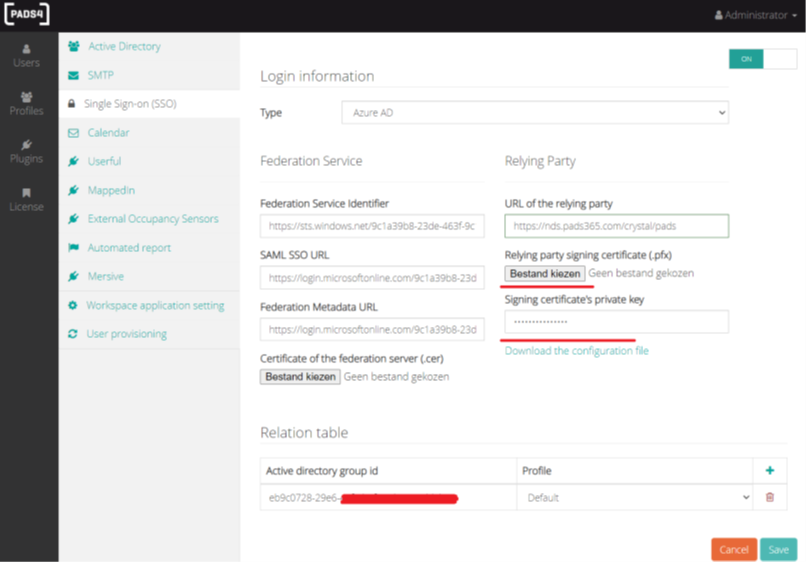
For the “relying party signing certificate”, we suggest using the certificate that you use for your HTTPS configuration. “Convert that certificate to .pfx. “
The below section is where the certificate and private key need to be configured.
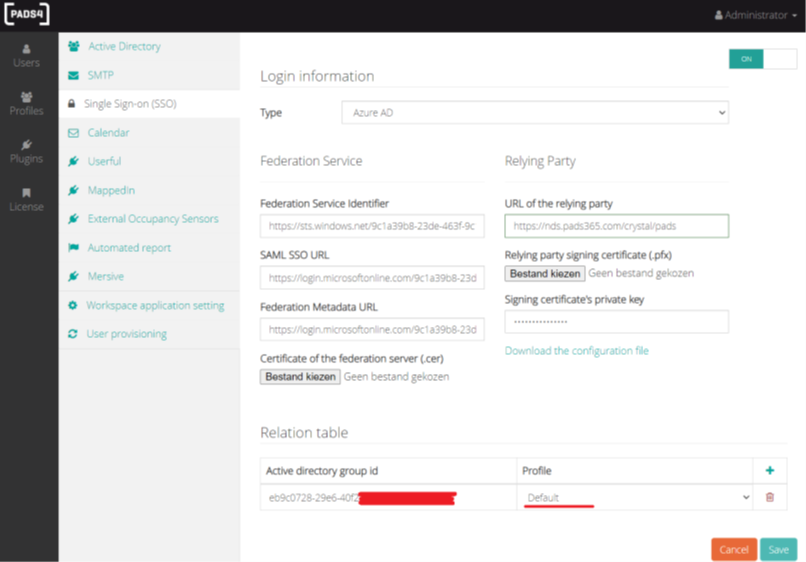
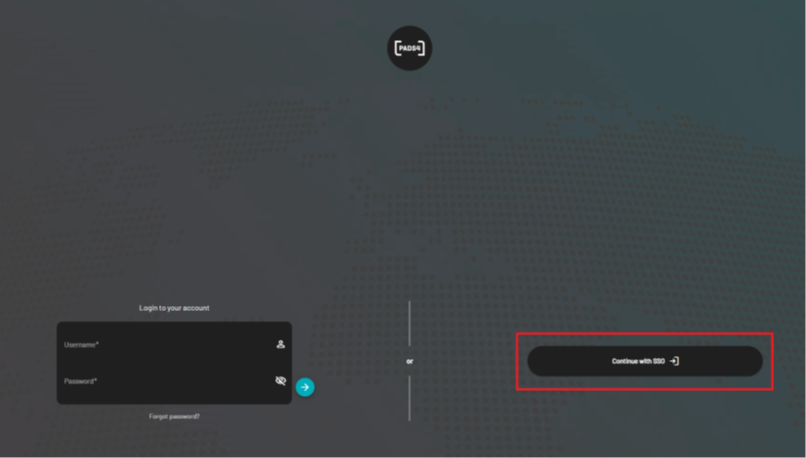
When you configure the**“Relation Table”** in CMS Admin for SSO, seta profile that you created for the SSO users or group in relation totheir privilege level.Example below:Save the configuration then log out and you should now see thebelow “Single Sign On” as an option :