PADS4 version 2026.1 adds support for the Microsoft Graph API.
EWS in Exchange Online will be End of Life in Q4 - 2026. If you have an existing application registered as below, migrate it to use the Microsoft Graph API as follows:Make sure to add the following permissions to your existing application registration:
After updating the permissions, you must grant admin consent to the application before the service can authenticate successfully.Within PADS4 - CMS 1.0 Admin, you must then update the Calendar configuration: 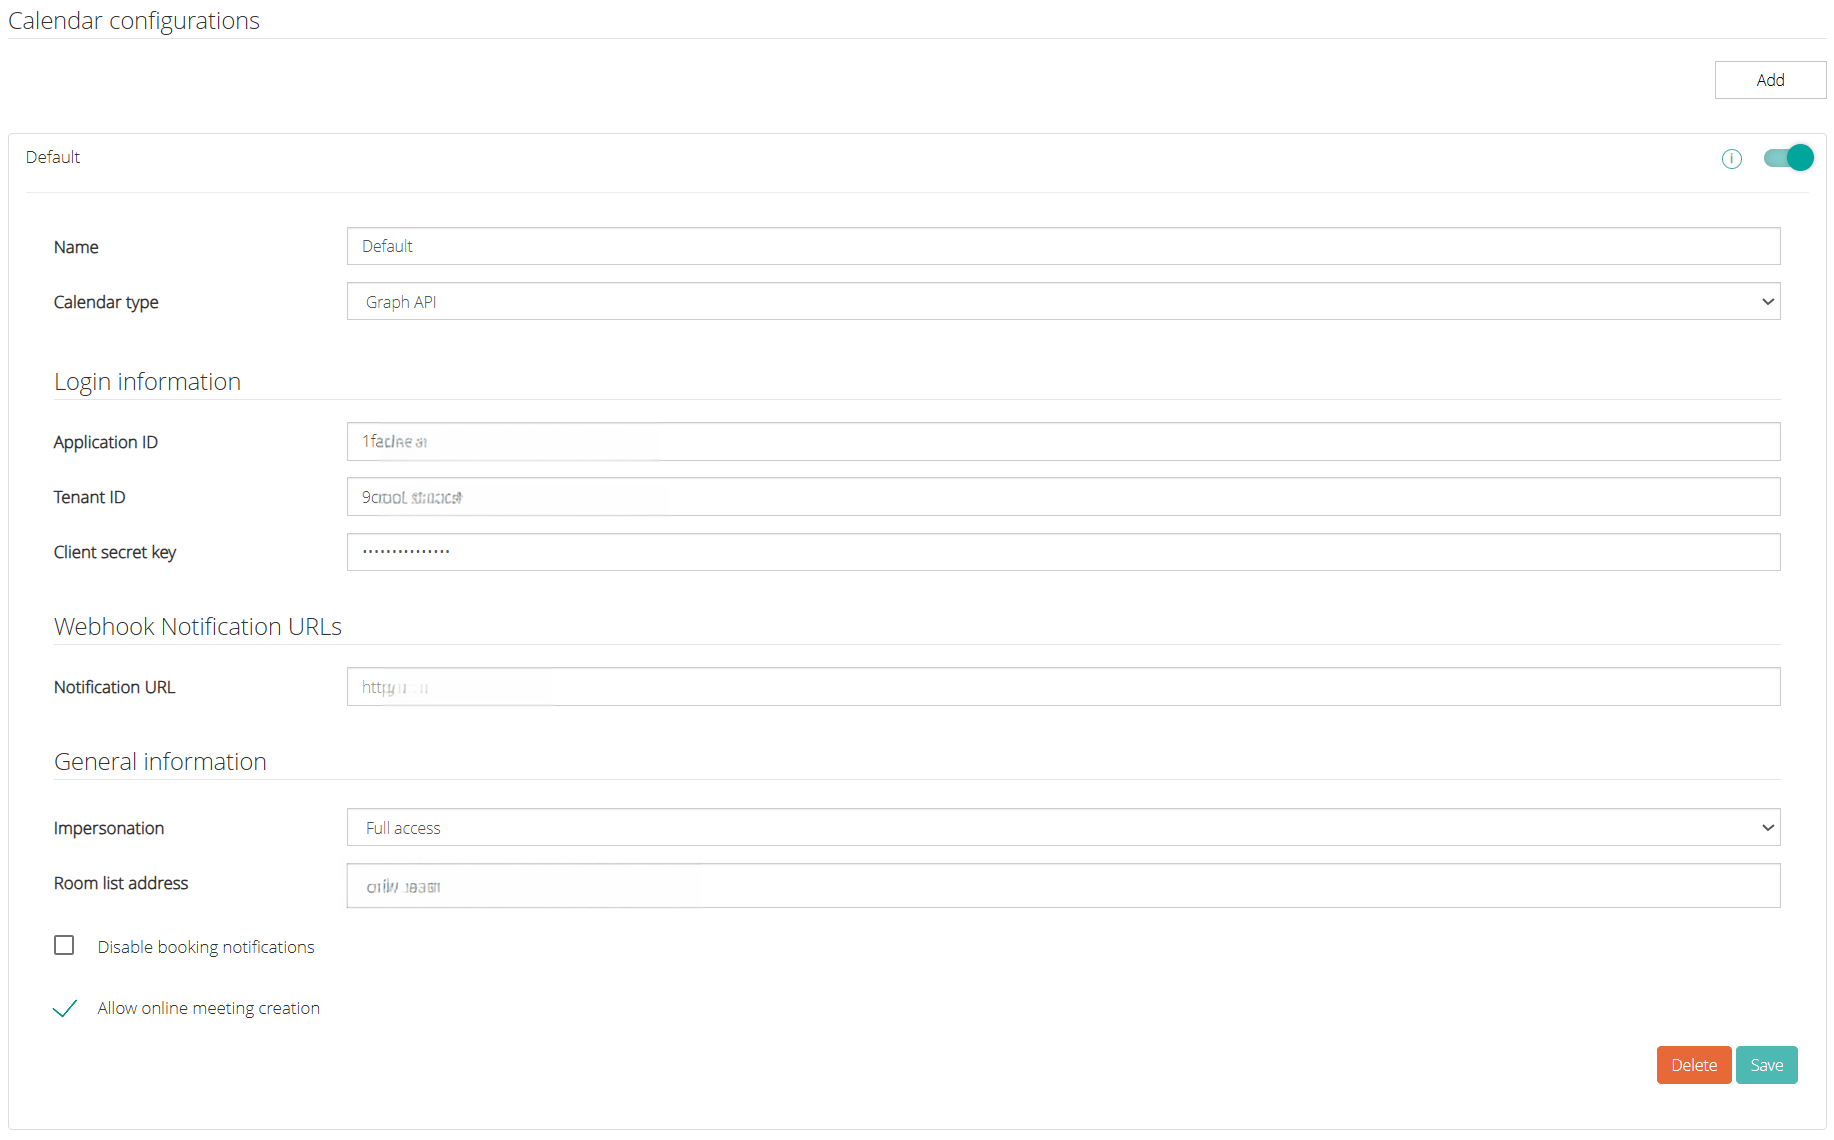
| Permission | Required | Description |
|---|---|---|
| Calendars.ReadWrite | Yes | Read and synchronize room calendar events. |
| Place.Read.All | Optional | Required only when importing rooms from Microsoft Places or Room Lists. |
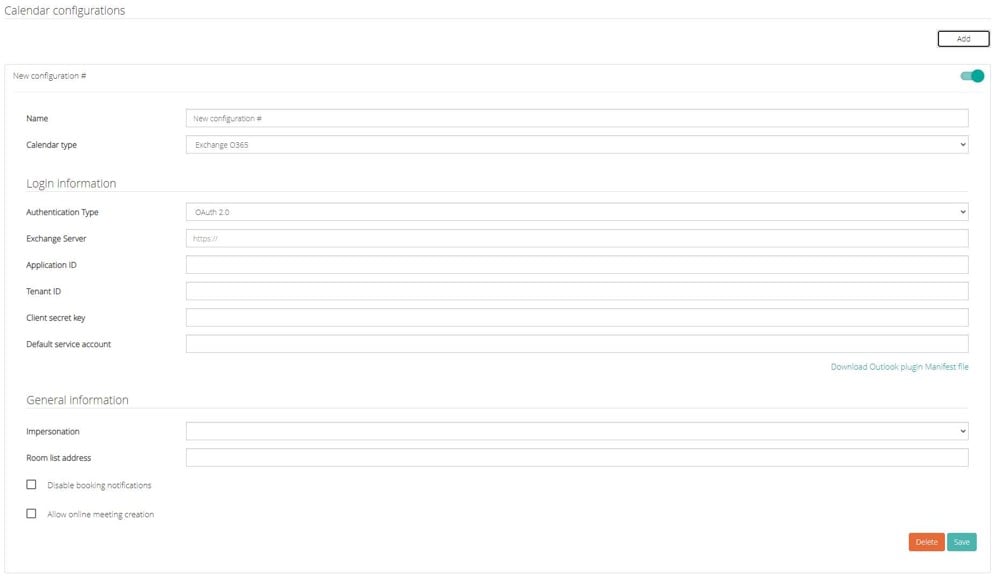
- Change the calendar provider from Exchange O365 to Graph API.
- Configure the Webhook Notification URL, if required. This setting is optional when the notification endpoint uses the same DNS host name already configured for the application.
- If you deploy PADS4 in a secure environment, make sure the following domain is accessible on the network: graph.microsoft.com
The webhook notification endpoint must be publicly accessible over HTTPS to receive Microsoft Graph change notifications.
Register the application
- Open a browser and navigate to the Microsoft Entra ID admin center and log in using a personal account (Microsoft account) or a work or school account.
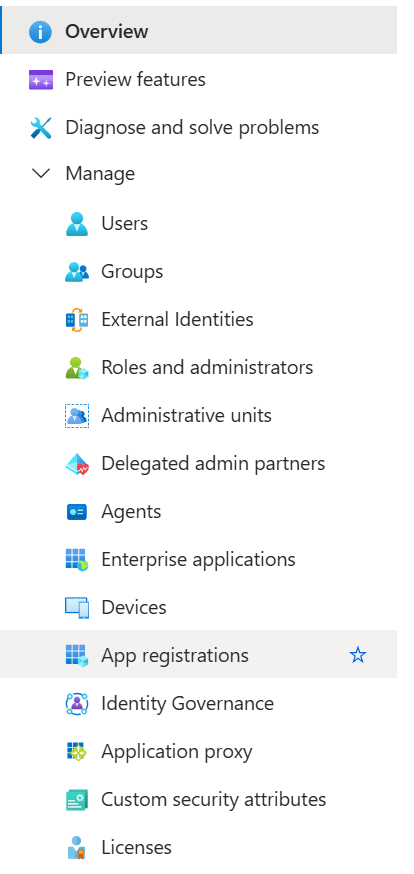
- Select Identity in the left-hand navigation, then select App registrations under Applications.
- Click New registration. On the Register an application page, set the values as follows.
a. Set Name to a friendly name for your app.
b. Set Supported account types to the choice that makes sense for your scenario.
c. For Redirect URI, change the dropdown to Public client (mobile & desktop) and set the value to: urn:ietf:wg:oauth:2.0:oob
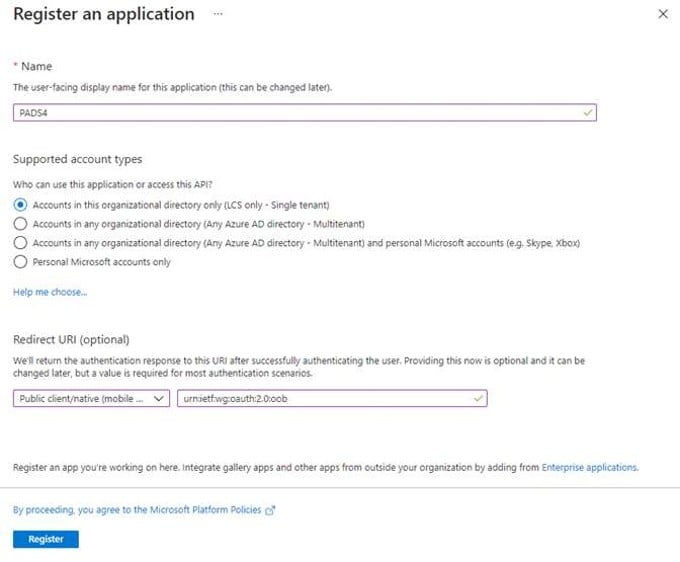
- Click Register. On the next page, copy the values of the Application (client) ID and Directory (tenant) ID and save them. You need them later to configure the calendar plugin in CMS.
Configure for app-only authentication
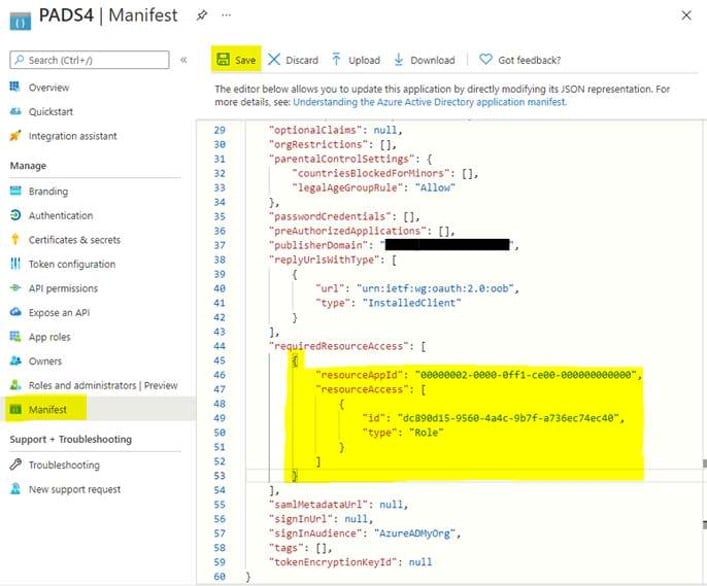
To use application permissions, follow these additional steps.- Select Manifest in the left-hand navigation under Manage.
- Locate the requiredResourceAccess property in the manifest, and add the following inside the square brackets ([]):
{ "resourceAppId": "00000002-0000-0ff1-ce00-000000000000", "resourceAccess": [ { "id": "dc890d15-9560-4a4c-9b7f-a736ec74ec4e", "type": "Role" } ]}
- Click Save.
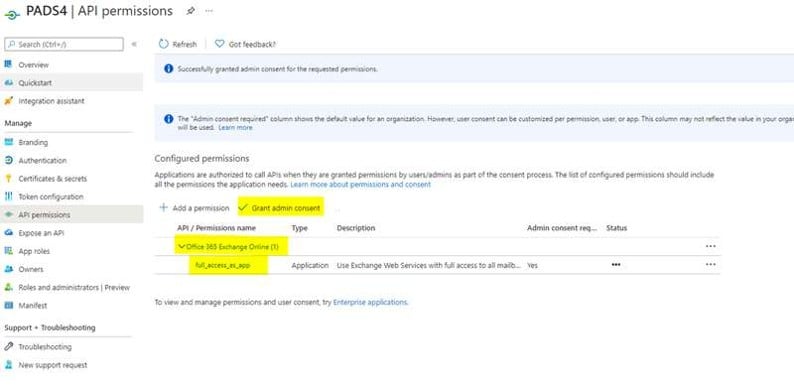
- Select API permissions under Manage. Confirm that the full_access_as_app permission is listed.
- Click Grant admin consent for org and accept the consent dialog.
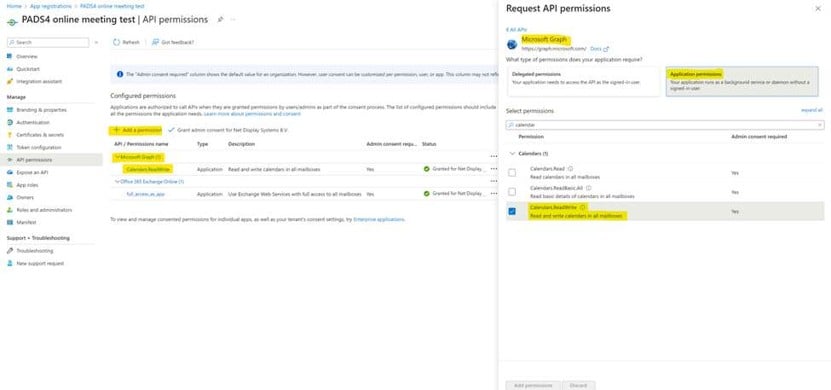
- Click Add a permission.
- Select the Microsoft Graph > Calendars.ReadWrite permission, then click Add.
- Grant admin consent to that permission.
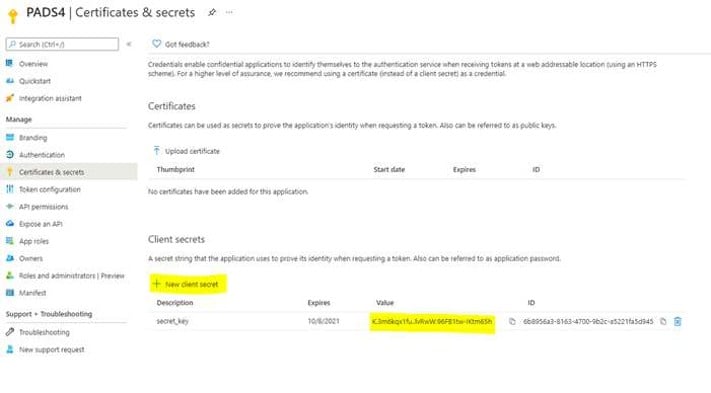
- Select Certificates & Secrets in the left-hand navigation under Manage.
- Click New client secret, enter a short description, and click Add.
- Copy the Value of the newly added client secret and save it. You need it later when configuring the calendar plugin in CMS.
Create a service account user
- Log in to your Office 365 as an administrator.
- Navigate to Office 365 admin center > USERS > Active Users.
- To add a new user, click the ”+” icon. The create new user account page appears.
- On the create new user account page, complete the required information.
By default, Exchange changes the subject of the meeting to the organizer’s name. To change this behavior, change the Calendar Processing of the rooms that you use.
- Connect to Exchange Online PowerShell. For details, see Connect to Exchange Online PowerShell.
- Run the following command, replacing <ResourceMailbox> with the name of your room.
Manage restricted access (if required)
If you added an application access policy, you first need to include the service account in the restricted access distribution group.
- Connect to Exchange Online PowerShell. For details, see Connect to Exchange Online PowerShell.
- Identify the app’s client ID and a mail-enabled security group to restrict the app’s access.
- Create an application access policy.
- Test the newly created application access policy.
Changes to application access policies can take up to 30 minutes to take effect in EWS API calls.
Manage room list (for retrieving rooms to import)
- To import rooms in Workspace, create a room list and add the rooms that you want to import to it. Otherwise, you need to add the rooms to Workspace manually. Using a room list is more convenient than adding rooms manually.
- A room list should not contain more than 100 rooms. A Room List request returns a maximum of 100 rooms. If you plan to have more, split them into multiple room lists.
- Connect to Exchange Online PowerShell. For details, see Connect to Exchange Online PowerShell.
- Use the Exchange Management Shell to create a room list:
- Use the Exchange Management Shell to add a room to a room list:
- To check that the room list exists, run the following command:
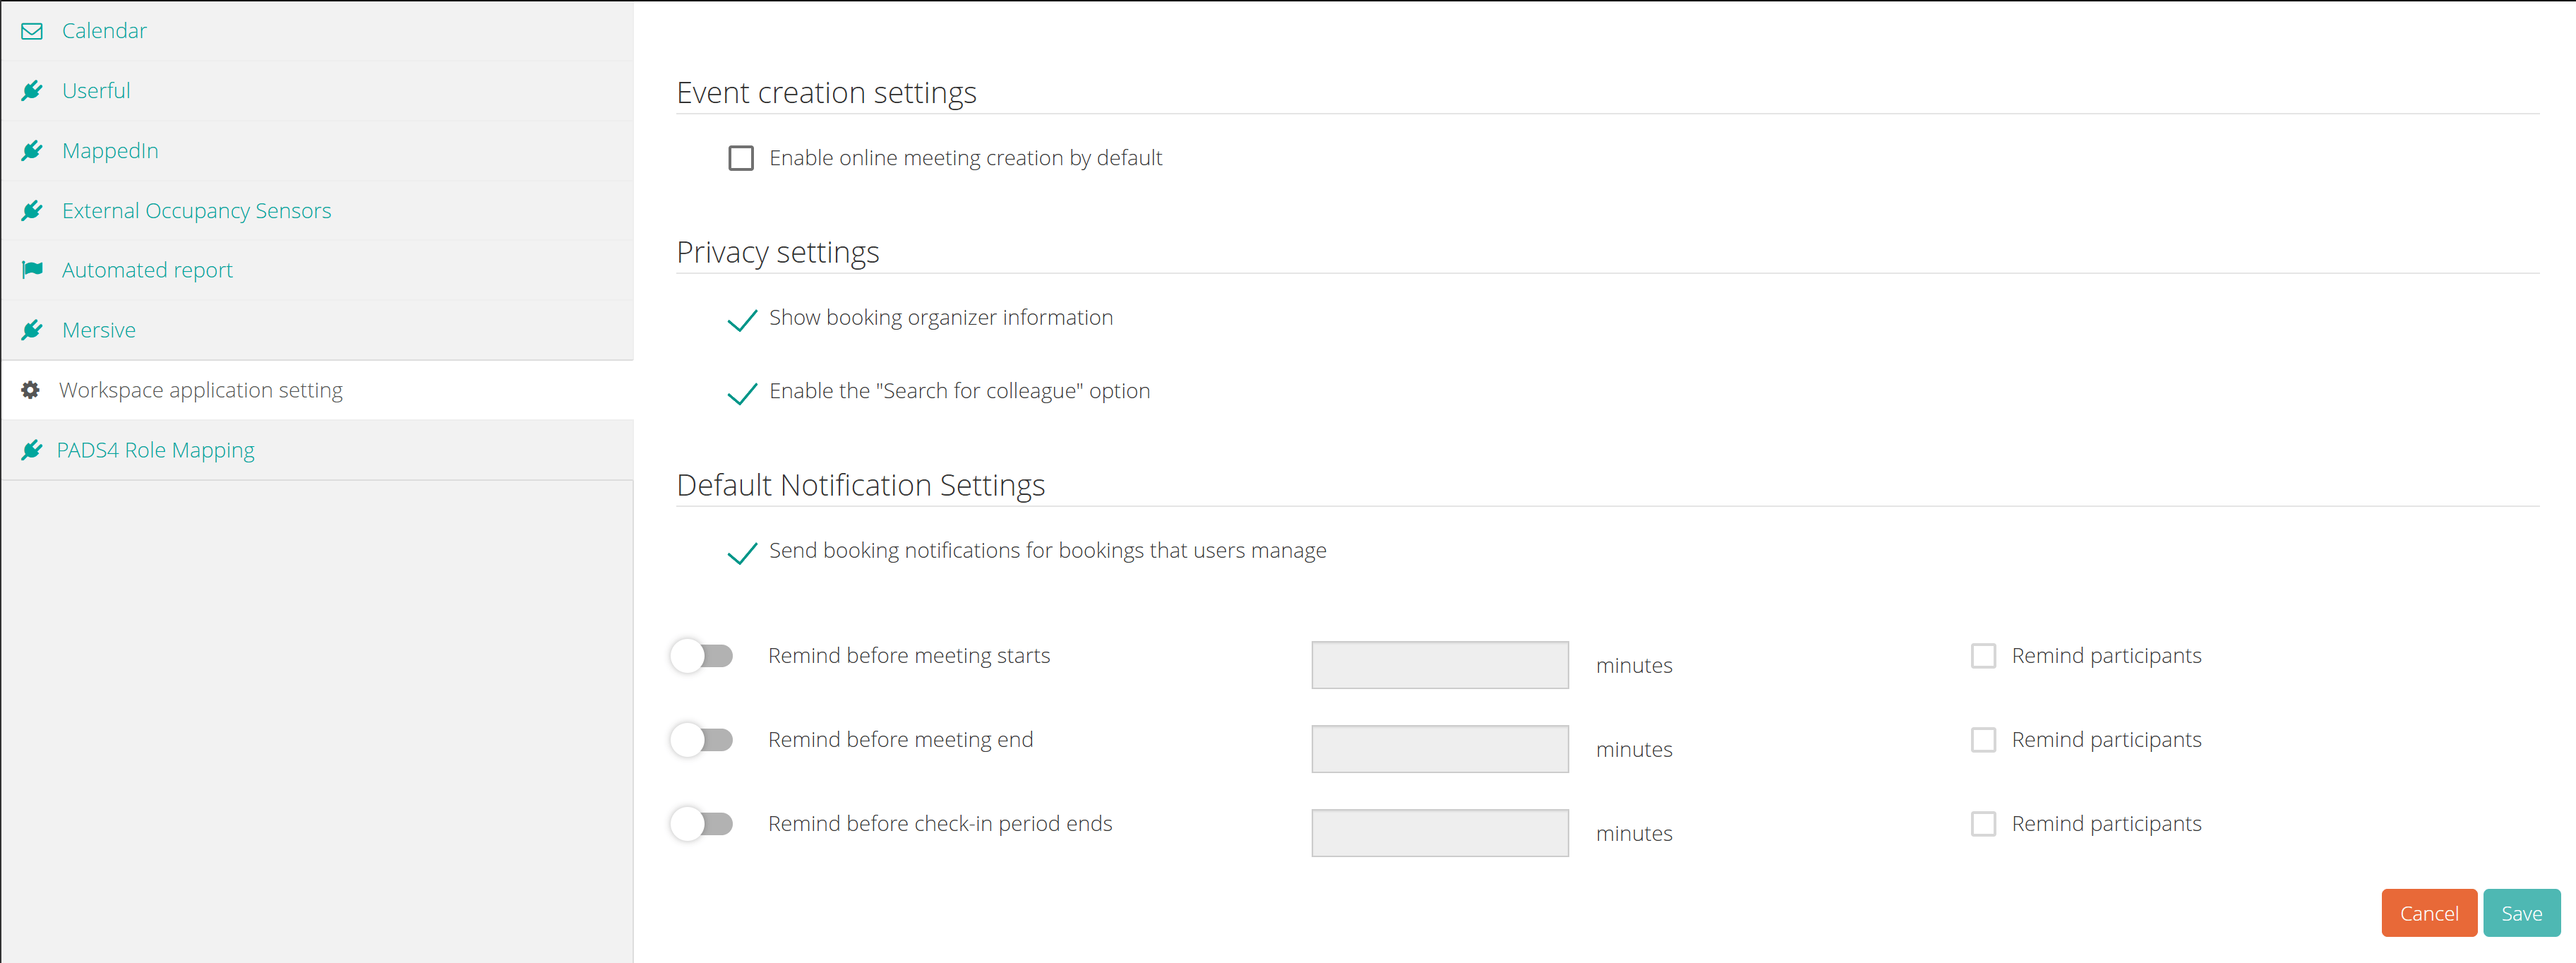
- Go to CMS Administration.
- Open Workspace application settings.
- Select Enable online meeting creation by default.
- Click Save.
Create an event with a Teams meeting from Workspace
This option is only available if you selected a room that uses an external calendar configuration with that option set up. It is also available if your user is configured to use the external calendar configuration for user impersonation.
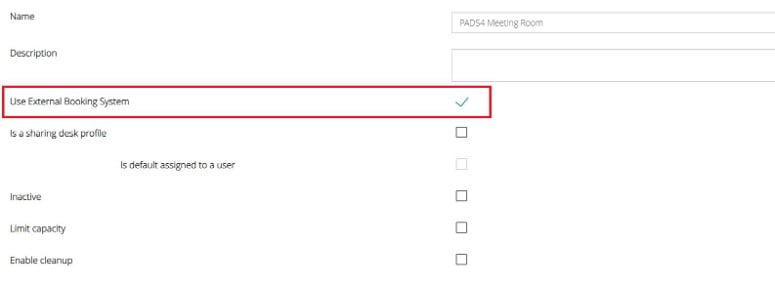
- To create a Teams meeting in Workspace, create an event and select the Teams meeting option while creating it.
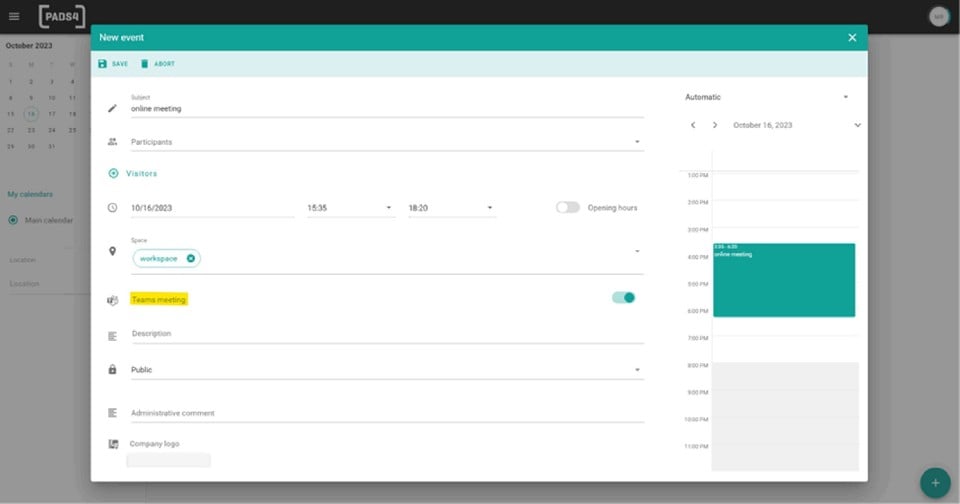
- After you create the event with the Teams meeting option turned on, it appears as shown below:
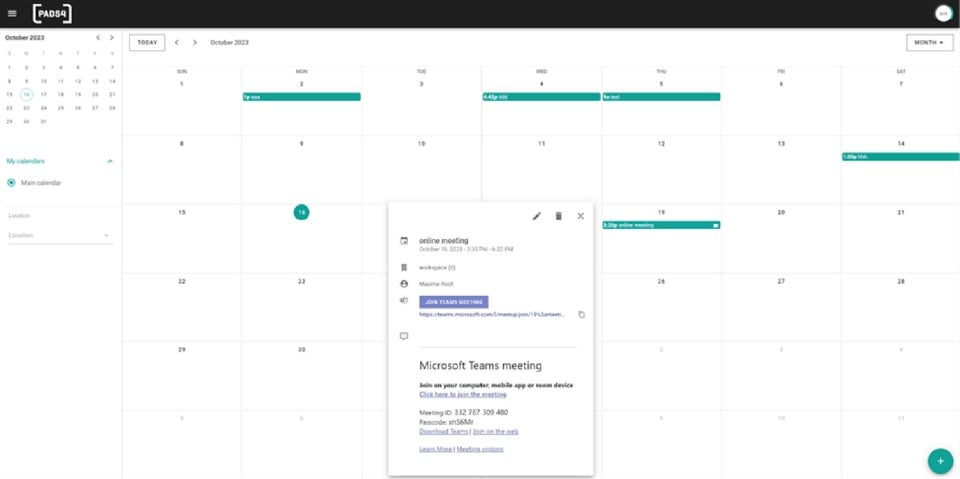
Impersonation
There are three operating modes, described below. Set the operating mode according to the desired results and your company’s security rules:
#1. Impersonation = Full access
With Full access impersonation, the reservation function behaves as follows:Booking from Outlook
- The reservation is made from the user account with the choice of the room and the guests.
- You can modify and delete this reservation from Outlook and Workspace.
- Changing and deleting the tablet reservation affects both the user and resource calendar.
Booking from Workspace
- The reservation is made from the user account with the choice of the room and the guests.
- You can modify and delete this reservation from Workspace and Outlook.
- Changing and deleting the tablet reservation affects both the user and resource calendar.
Booking from a tablet
- The reservation is made from the service account, which impersonates the connected user.
- The owner / organizer of the meeting is the logged in user.
- You can modify and delete this reservation from the tablet. Doing so affects the calendar of the user and the resource.
- You can edit, delete, or add participants using the user calendar (who owns this meeting).
#2. Impersonation = Resources only
This option requires that the service account has the right to impersonate all resources imported into PADS4 CMS. To manage this, grant the ApplicationImpersonation role to the user of the service account using this PowerShell script:Booking from Outlook
- The reservation is made from the user account with the choice of the room and the guests.
- You can modify and delete this reservation from Outlook and Workspace.
- Changing and deleting the tablet reservation only affects the resource calendar.
Booking from Workspace
- The reservation is made from the user account with the choice of the room and the guests.
- You can modify and delete this reservation from Workspace and Outlook.
- Changing and deleting the tablet reservation only affects the resource calendar.
Booking from a tablet
- The reservation is made from the service account, which impersonates the resource.
- The owner / organizer of the meeting is the resource. The logged in user is added as a participant.
- You can modify and delete this reservation from the tablet. Doing so affects the calendar of the user and the resource.
- You can edit, delete, or add participants using the resource calendar (who owns this meeting).
#3. Impersonation = None
With None impersonation, the reservation function behaves as follows:Booking from Outlook
- The reservation is made from the user account with the choice of the room and the guests.
- You can modify and delete this reservation from Outlook.
- Changing and deleting the tablet reservation only affects the resource calendar.